Dependency Firewall offer: 50% off your base fee for 3 months + €100 usage credit.Start trialSee what’s new

SBOM Observer

Analyze every SBOM you build or buy. Monitor each release for vulnerabilities and license issues, and enforce your policies in CI/CD.

The dashboard in the live demo. No signup needed.

Continuous monitoring of all your SBOMs

SBOMs from your builds, suppliers and existing tools go into one index. SBOM Observer checks every component against new advisories as they are published, so you see what a release ships and what affects it.

All your SBOMs in one graph

Every SBOM, VEX and attestation you add is joined into one index of components, releases and enrichment data. Policies run against the whole model, and the source documents stay intact for audit.

  • Applications · Each holds its releases, their SBOMs and supplier components.
  • Components · Deduplicated across SBOMs. A library used by ten applications is one record.
  • Enrichment · Vulnerabilities, licenses, OpenSSF Scorecard values and SLSA provenance.
  • Relationships · Direct and transitive paths from an advisory to every release that ships it.
  • Attestations · VEX and SLSA provenance stored next to the release.

See every release a vulnerability reaches

A CVE list tells you which package is vulnerable. SBOM Observer tells you which of your applications and releases ship it, and through which dependency.
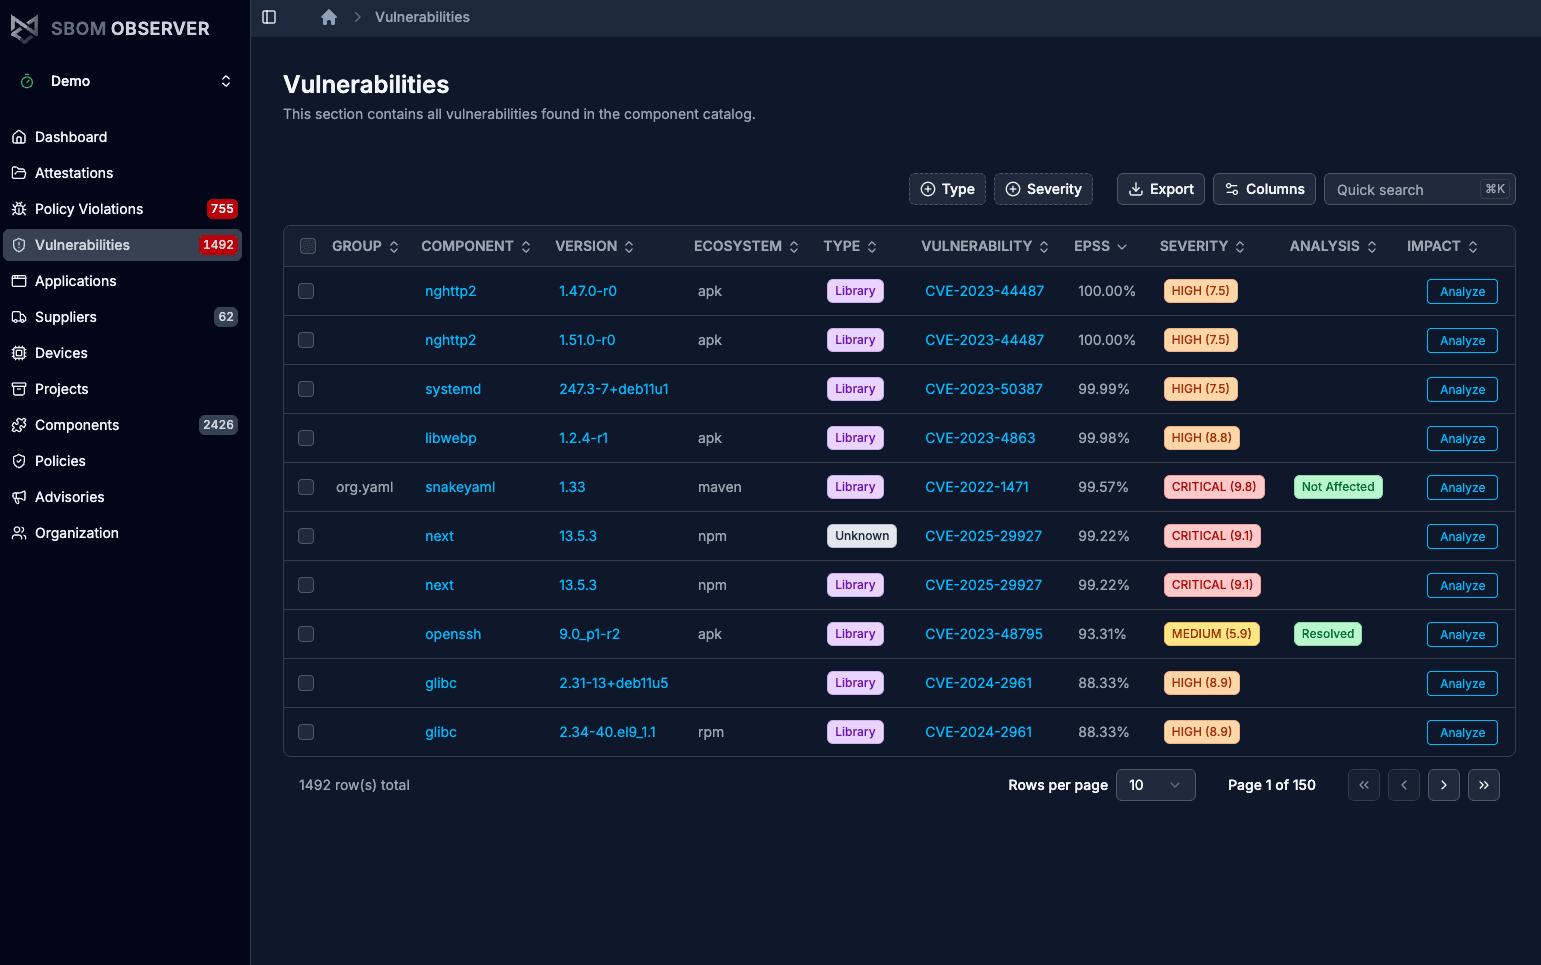
  • Every tracked component is monitored against OSV, GitHub Advisories and NVD. A new advisory shows up against the releases it affects.
  • The impact graph follows the dependency path from the vulnerable package to each application that ships it.
  • Severity and EPSS on every finding, so the likely exploits come first.
  • Dashboards per application, with the trend across releases.
Impact graph for CVE-2023-4863 in libwebp, traced through the dependencies that pull it in
Vulnerabilities across all components, with EPSS, severity, VEX analysis status such as Not Affected and Resolved, and an Analyze action

Decide which vulnerabilities apply

A match on a package name says little about your product. Review each finding once, record the decision as VEX and keep it with the release.

  • Record a VEX state, a justification and a response on each finding, with an owner and notes.
  • Findings marked not affected drop out of the queue and stay linked to the decision.
  • Export CISA VEX with the release.
  • Import VEX from a supplier to apply their decisions to their components.

Fail the build on a policy violation

Define a policy once and it applies to your own builds and to every supplier SBOM you upload.

  • Fail a build on a CVE above your CVSS and EPSS thresholds, or on a disallowed license.
  • Check SBOM quality, for example the NTIA minimum elements such as supplier name and version.
  • Build policies visually or write them in Rego or JavaScript. The engine is based on Open Policy Agent.
  • Run the Observer CLI in GitHub Actions, GitLab CI, Jenkins, Azure DevOps, CircleCI or any CI that runs a shell step.
build job in CI
# Generate an SBOM for this build
observer fs -o sbom.cdx.json .
 
# Evaluate your policies. Exits non-zero on a violation
observer analyze sbom.cdx.json
 
# Upload for monitoring when the build passes
observer upload sbom.cdx.json
Failed

Library Vulnerabilities EPSS/VEX

spring-beans 5.3.17: CVE-2022-22965 with CVSS 9.8 and EPSS 0.98 is not tolerated for a library
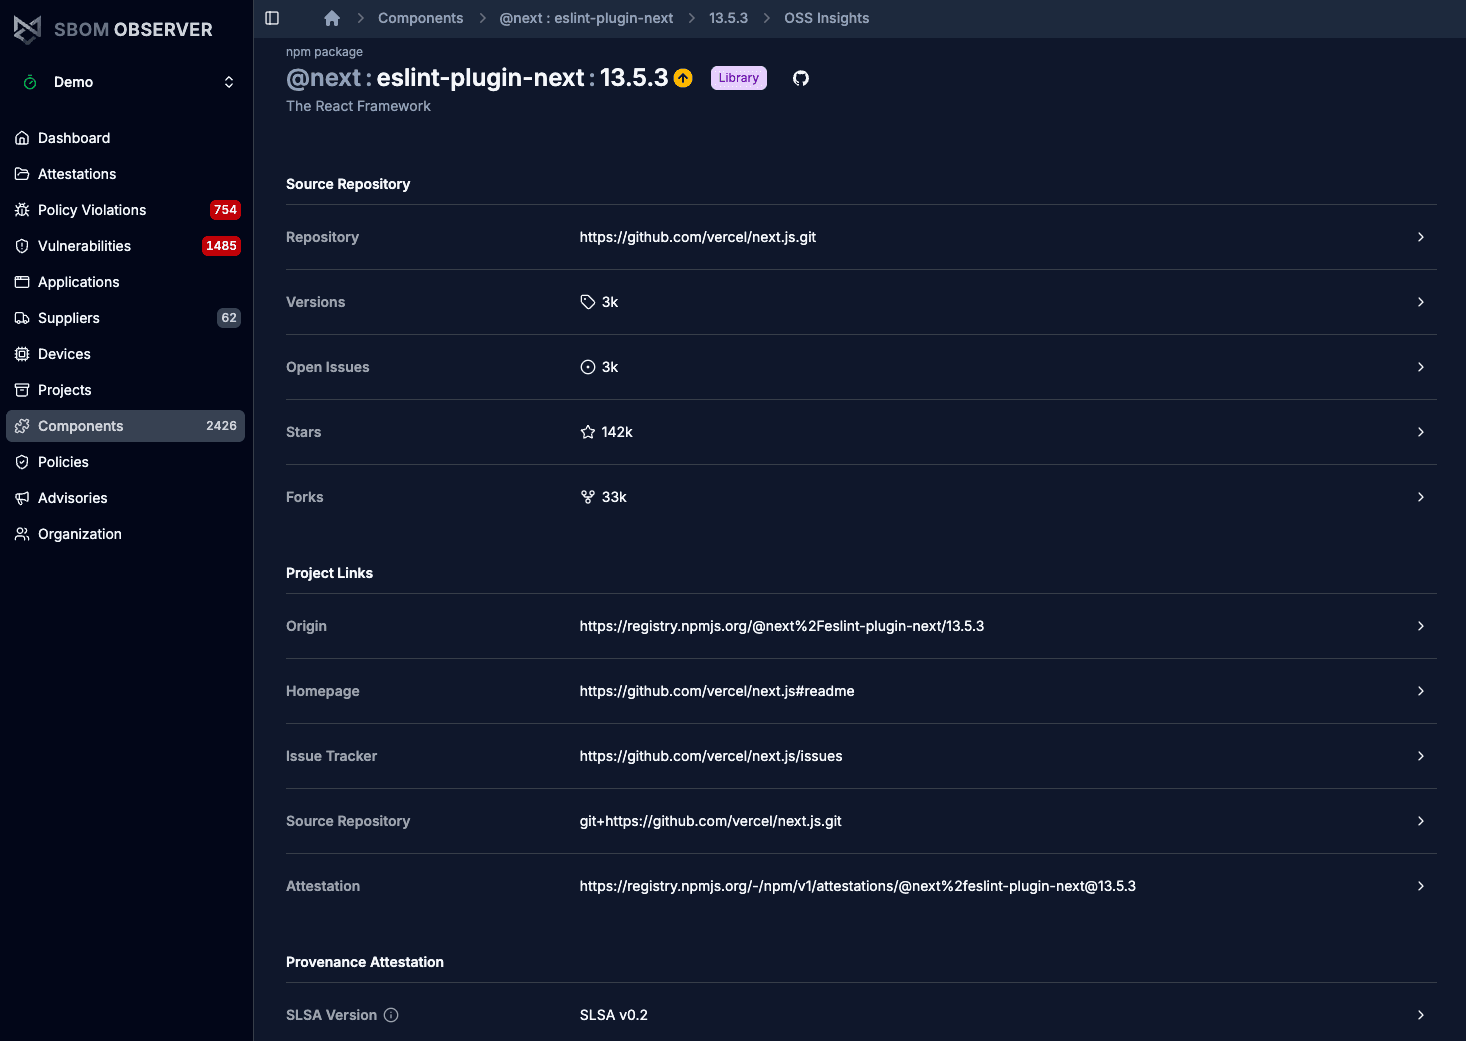
Component page with source repository, project links and SLSA provenance
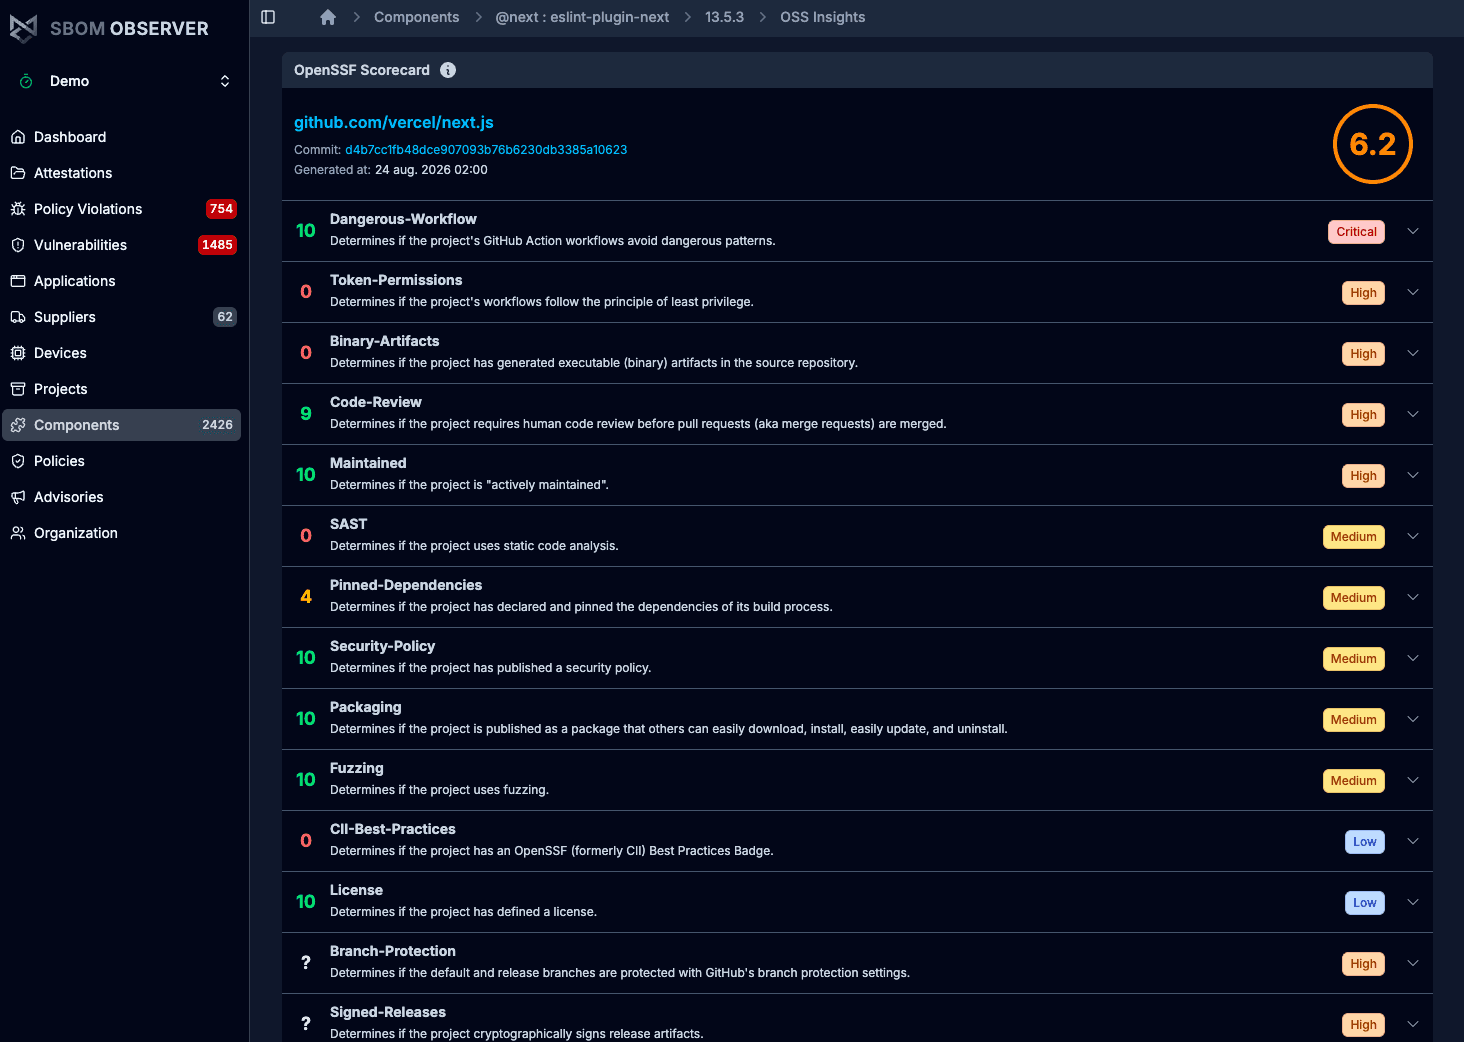
OpenSSF Scorecard checks for the component's source project

Component page with SLSA provenance, and the OpenSSF Scorecard for its source project

Know where each component comes from

Each component page has an OSS Insights view: how the package was built and how its source project is run, next to its vulnerabilities and policy results.

  • SLSA provenance when the package has it: who built it, from which repository, workflow run and build config.
  • The OpenSSF Scorecard for the source repository, with each check scored.
  • Versions, dependencies, a dependants graph and attestations per component.
  • Export or share the SBOM of a single component.

Container SBOMs broken down by layer

A container SBOM on its own is a flat list of components. SBOM Observer sorts it by base layer, system package and application dependency.
  • Base image layers, operating system packages and application dependencies are separated in the component graph.
  • Each component is traced back to the layer that introduced it.
  • A finding points to a component and its layer, so you know whether to rebuild on a new base image or update a dependency.
A Keycloak container image broken down by layer, with components and vulnerabilities per layer
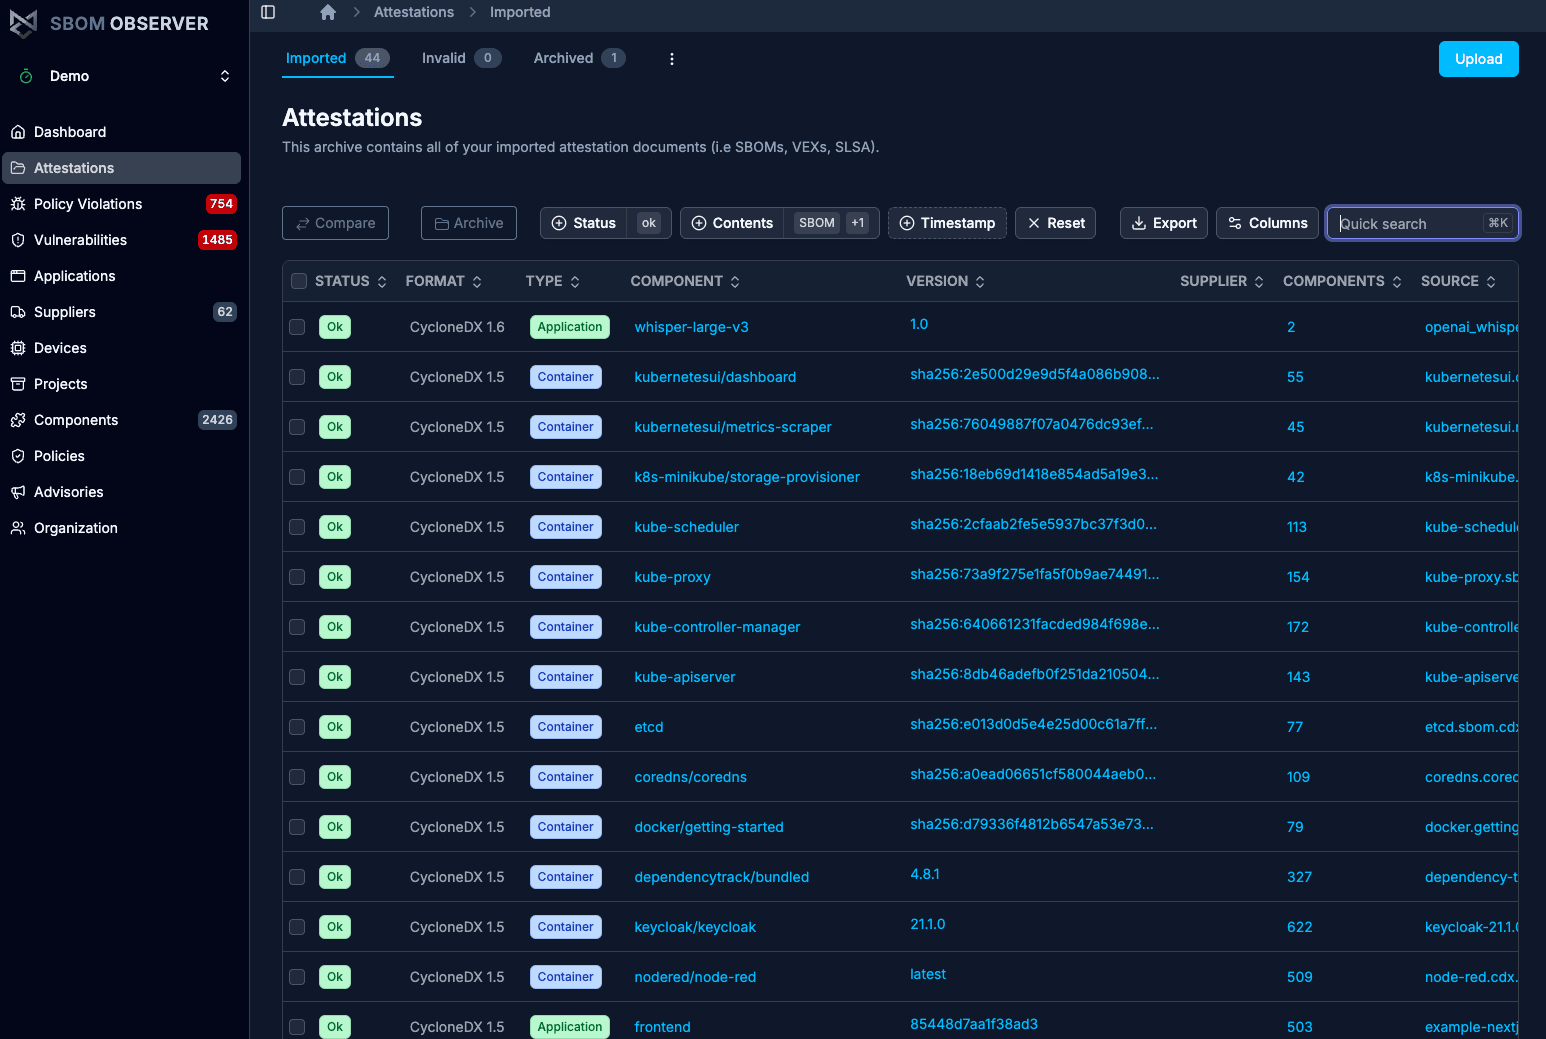
All attestations: SBOM, VEX and SLSA provenance

Every release keeps its evidence

SBOMs come in from your pipelines and your suppliers, and stay with the release they describe.

From CI/CD
The Observer CLI generates an SBOM, evaluates policy and uploads it from every pipeline run.
By upload
Supplier SBOMs and one-off files uploaded in the browser.
Kept per release
SBOM, VEX and SLSA provenance stay attached to the release they describe, version after version.

Evidence for EU regulation

SBOM Observer keeps the SBOM and vulnerability records that compliance work for these regulations depends on.

Cyber Resilience Act (CRA)
A machine-readable SBOM per release, vulnerability status across supported versions and a record of the policy checks each release passed.
NIS2
Supply chain risk evidence: which supplier components you run and what is known about them.
DORA
Third-party ICT risk evidence for financial entities, built from vendor SBOMs.
EO 14028 (US)
Collect, check and keep the SBOMs your software vendors deliver.

CRA dates and obligations are on the Trust Repository page.

What is in SBOM Observer

Every plan includes all of it. Enterprise adds scale, access control and deployment options.

SBOM management
Create, import and manage SBOMs in CycloneDX 1.3 and later and SPDX 2.2 and later, in JSON, XML, YAML and tag-value.
Vulnerability detection
Applications, components and containers monitored against GitHub Advisories, OSV and NVD.
Exploit prediction scoring
EPSS next to CVSS on every finding, to rank remediation by how likely an exploit is.
CISA VEX
Record whether a vulnerability affects your product, and share it as VEX with customers and partners.
SLSA support
Check that the source you rely on is the code that was built, from SLSA provenance attestations.
Policy engine
Built on Open Policy Agent. A visual builder, or Rego and JavaScript for policy as code.
CI/CD
The Observer CLI generates, checks and uploads SBOMs from any pipeline and fails the build on a violation.
Container analysis
Container SBOMs broken down by base layer, system package and application dependency.
OpenSSF Scorecard
Project health checks for the source repository of each component.
Impact analysis
Dependency graphs from a vulnerable package to every application and release that ships it.
Deployment
Managed SaaS in the EU, or on-premises on the Enterprise plan, including air-gapped.

SBOM Observer and Trust Repository

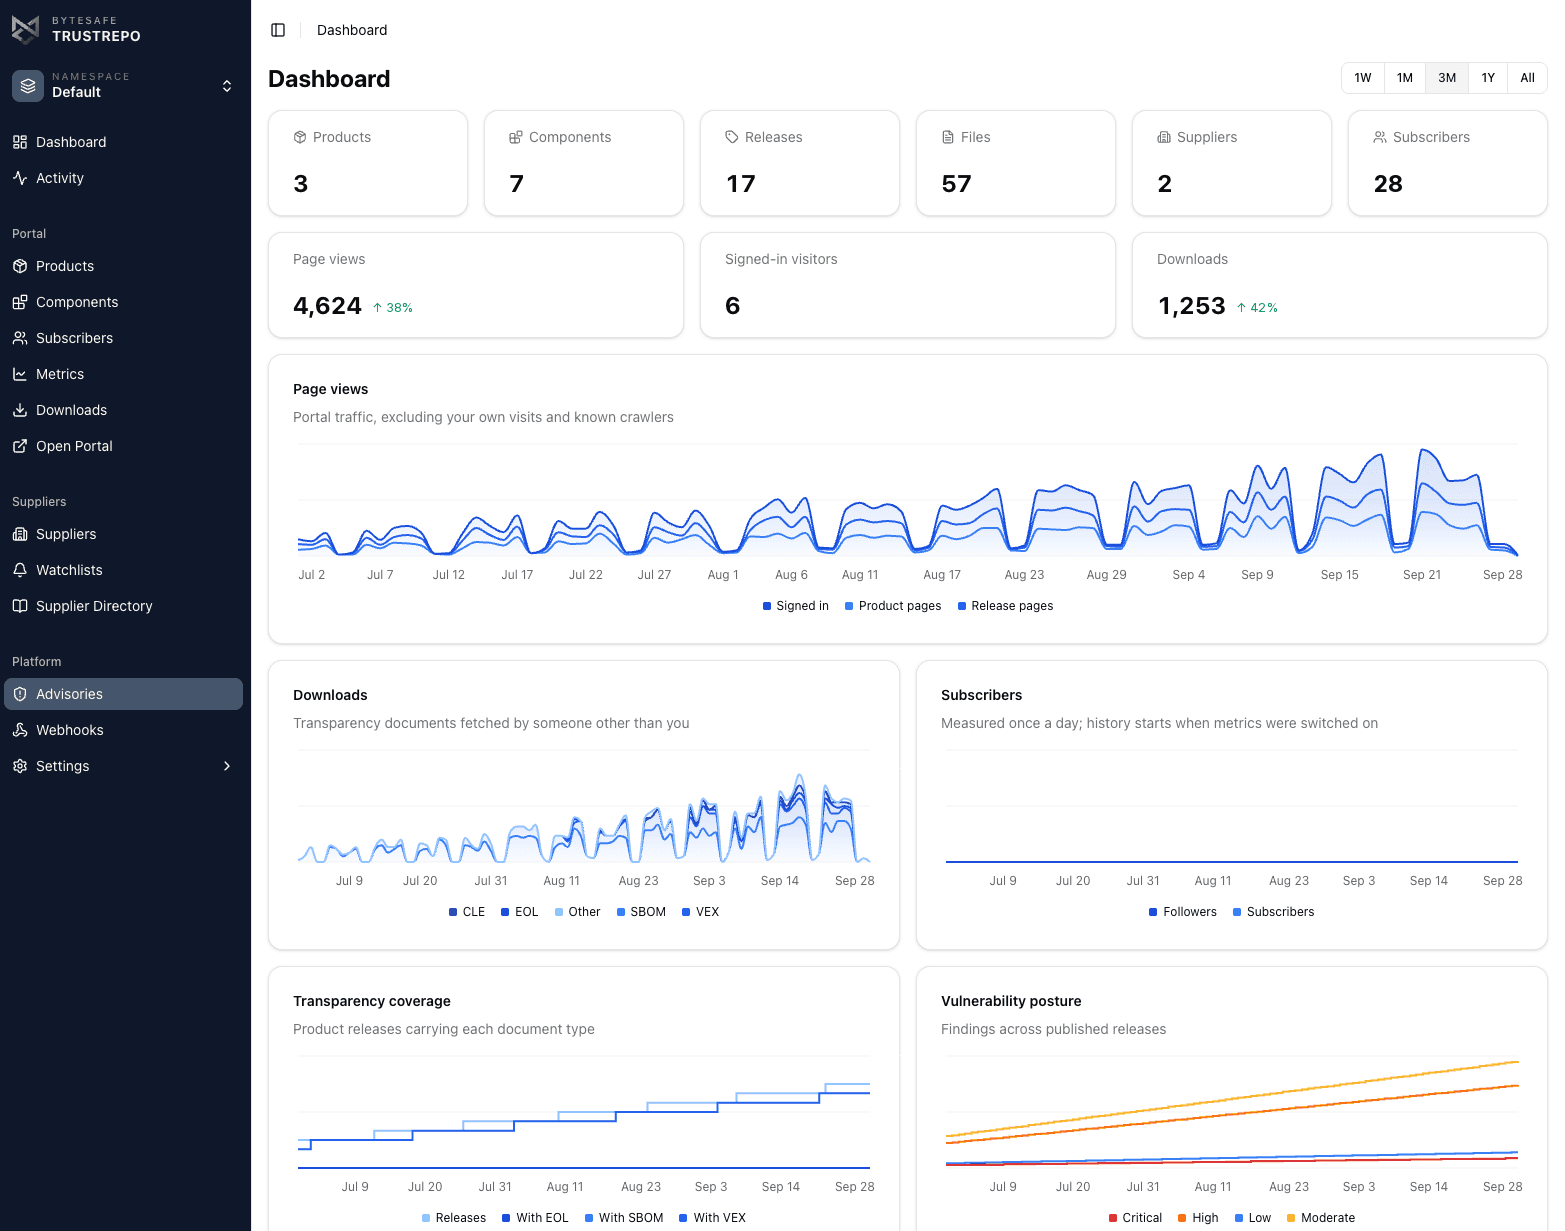
Trust Repository collects software transparency documents from your suppliers and publishes yours to your customers. SBOM Observer adds in-depth analysis and continuous monitoring across your portfolio.

Trust Repository

The exchange with suppliers and customers

  • Collect SBOM, VEX and support dates from suppliers
  • Publish yours per release on a Trust Portal
  • Vulnerabilities and SBOM quality issues per release
See Trust Repository

SBOM Observer

In-depth analysis and continuous monitoring

  • Impact analysis across applications and releases
  • Custom policies enforced in CI/CD
  • VEX review with supplier import and export

Frequently asked questions

Does SBOM Observer help with EU regulations such as the CRA?
Yes, for the CRA, NIS2, DORA and the US EO 14028. It keeps what these frameworks ask you to produce: an SBOM per release, the vulnerability status of each component, VEX decisions and the policy results for each build. When an auditor or a customer asks about a release, you answer from that record.
Does SBOM Observer monitor SBOMs after upload?
Yes. Every component in every stored SBOM is monitored against GitHub Advisories, OSV and NVD. When a new advisory is published, it shows up against the applications and releases that ship the affected component.
Which SBOM formats does SBOM Observer accept?
CycloneDX 1.3 and later, and SPDX 2.2 and later, in JSON, XML, YAML and tag-value. Any generator that produces these works, including Syft, Trivy and cdxgen.
Can we use our current SCA tool with SBOM Observer?
Yes. Export CycloneDX or SPDX from it and upload the result. SBOM Observer adds monitoring, policy, VEX and release history on top of what the tool found.
Does SBOM Observer handle supplier SBOMs?
Yes. Upload a supplier SBOM and it goes through the same policies as your own. An SBOM that misses required fields, such as the supplier name, fails the NTIA minimum elements policy.
How does SBOM Observer relate to Trust Repository?
They are separate products. Trust Repository collects software transparency documents from your suppliers and publishes yours to your customers, and reports vulnerabilities and SBOM quality issues. SBOM Observer analyzes SBOMs in depth: impact across applications and releases, custom policies in CI/CD and VEX review.
Can we run SBOM Observer on-premises?
Yes. The Enterprise plan includes on-premises deployment, including air-gapped environments.
Where is SBOM Observer hosted?
In the EU. Bitfront is an EU company and has worked on software supply chain security since 2018.
Can we try SBOM Observer before we buy?
Yes. The live demo and the free SBOM Analyzer need no signup. To see it with your own SBOMs, book a demo with one of our engineers.

Bytesafe Platform

Software Supply Chain Security and Transparency

Three products that block risky packages at install, collect supplier transparency documents, and analyze them.

Four ways to start with SBOM Observer

Start with one file, click through the demo, talk to an engineer or sign up.

Free SBOM Analyzer

Upload one SBOM and see its quality issues, vulnerabilities, components and licenses. No signup.

Analyze an SBOM

Live demo

A shared SBOM Observer workspace with example projects, components, vulnerabilities and policies. No signup.

Open the live demo

Personal demo

Walk through SBOM Observer with one of our engineers. Bring your own SBOMs or use ours.

Book a demo

Sign up

Start on the Business plan: €69 per user per month, 1 namespace and 10 projects, hosted in the EU.

Sign up

Need SSO, on-premises or more than 10 projects? Compare Business and Enterprise.