SBOM Sharing
Publish SBOMs, VEX and support dates per release on a Trust Portal. Customers download what they need and subscribe to updates, and you decide which customer sees which product.
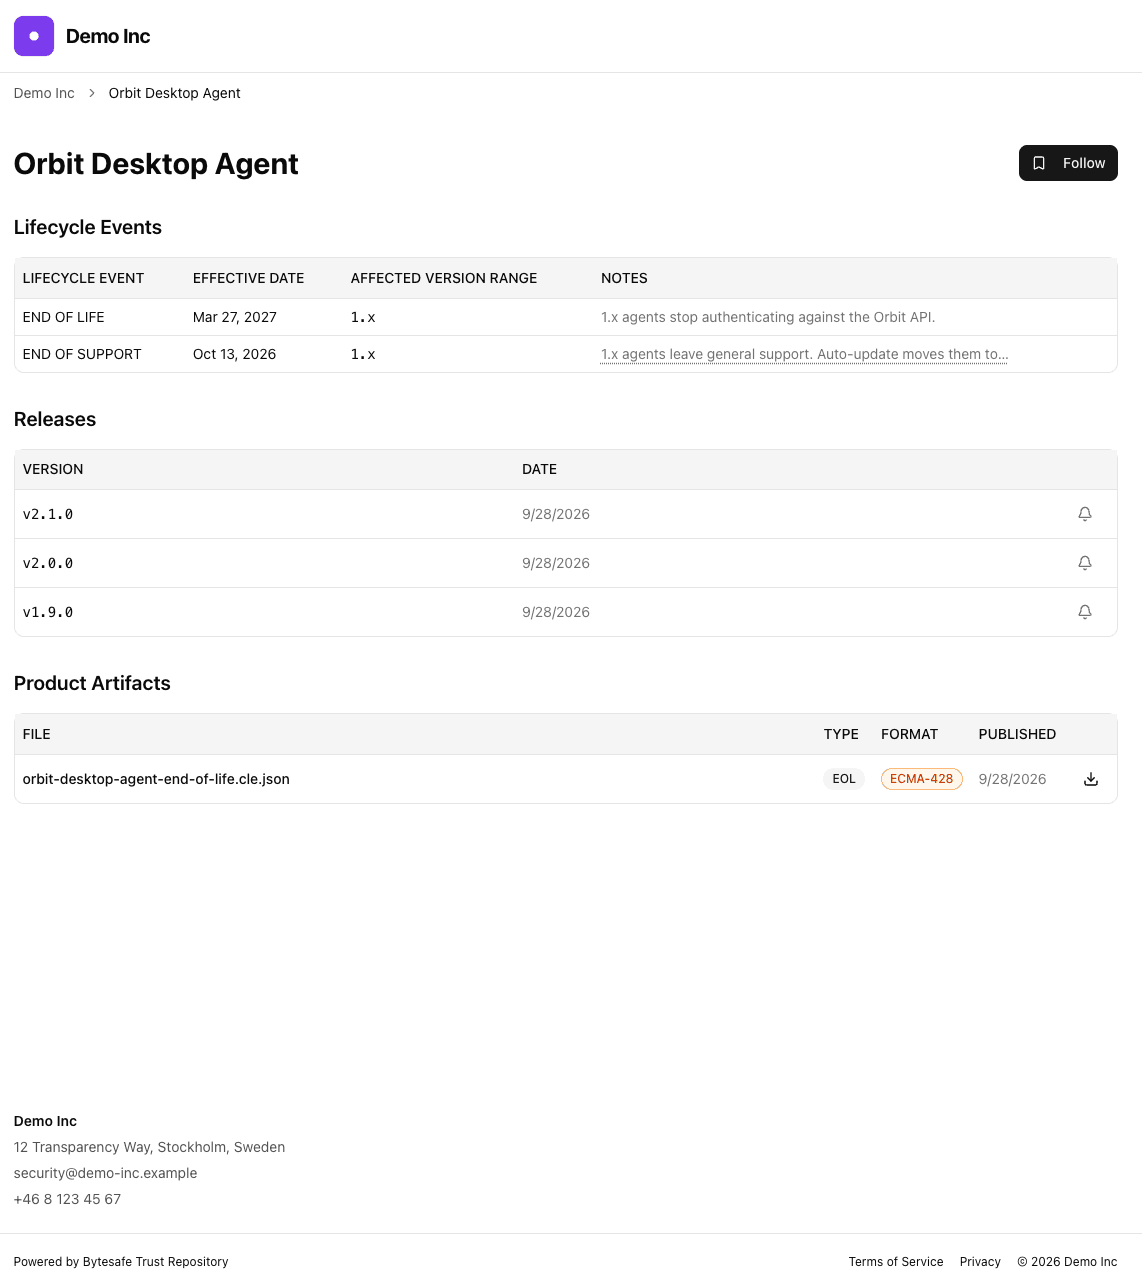
Every customer asks separately
Each customer sends its own questionnaire and wants SBOMs its own way. The same files go out by email again and again, and nobody tracks which version went to whom.
- The same request many times
- Security questionnaires and SBOM requests arrive from every customer, each in its own format.
- Every update is another email
- SBOMs go out as attachments, and each new release means sending them again.
- Some products are not for everyone
- Some products can be public. Others should only reach named customers.
- No record of who received what
- You cannot say which customer fetched which document, or when.
How it works with Trust Repository
1Upload from CI/CD
The release job uploads the SBOM with a token that can upload but not publish.
2Review and publish
Add VEX, build an aggregate SBOM or redact it, then publish the release.
3Customers subscribe
Subscribers see the new release on the portal. Webhooks tell your other systems.
Publishing is a separate step
Give CI a token that can upload but not publish. Someone reviews the release before customers see it. The REST API covers products, releases, files, VEX and lifecycle dates.
# Upload the SBOM this build producedcurl -X POST "$API/component-releases/$ID/artifacts?type=SBOM&name=sbom.json" \-H "Authorization: Bearer $UPLOAD_TOKEN" \-H "Content-Type: application/json" \--data-binary @sbom.json# Publish with a token that holds catalog:publishcurl -X POST "$API/component-releases/$ID/publish" \-H "Authorization: Bearer $PUBLISH_TOKEN"
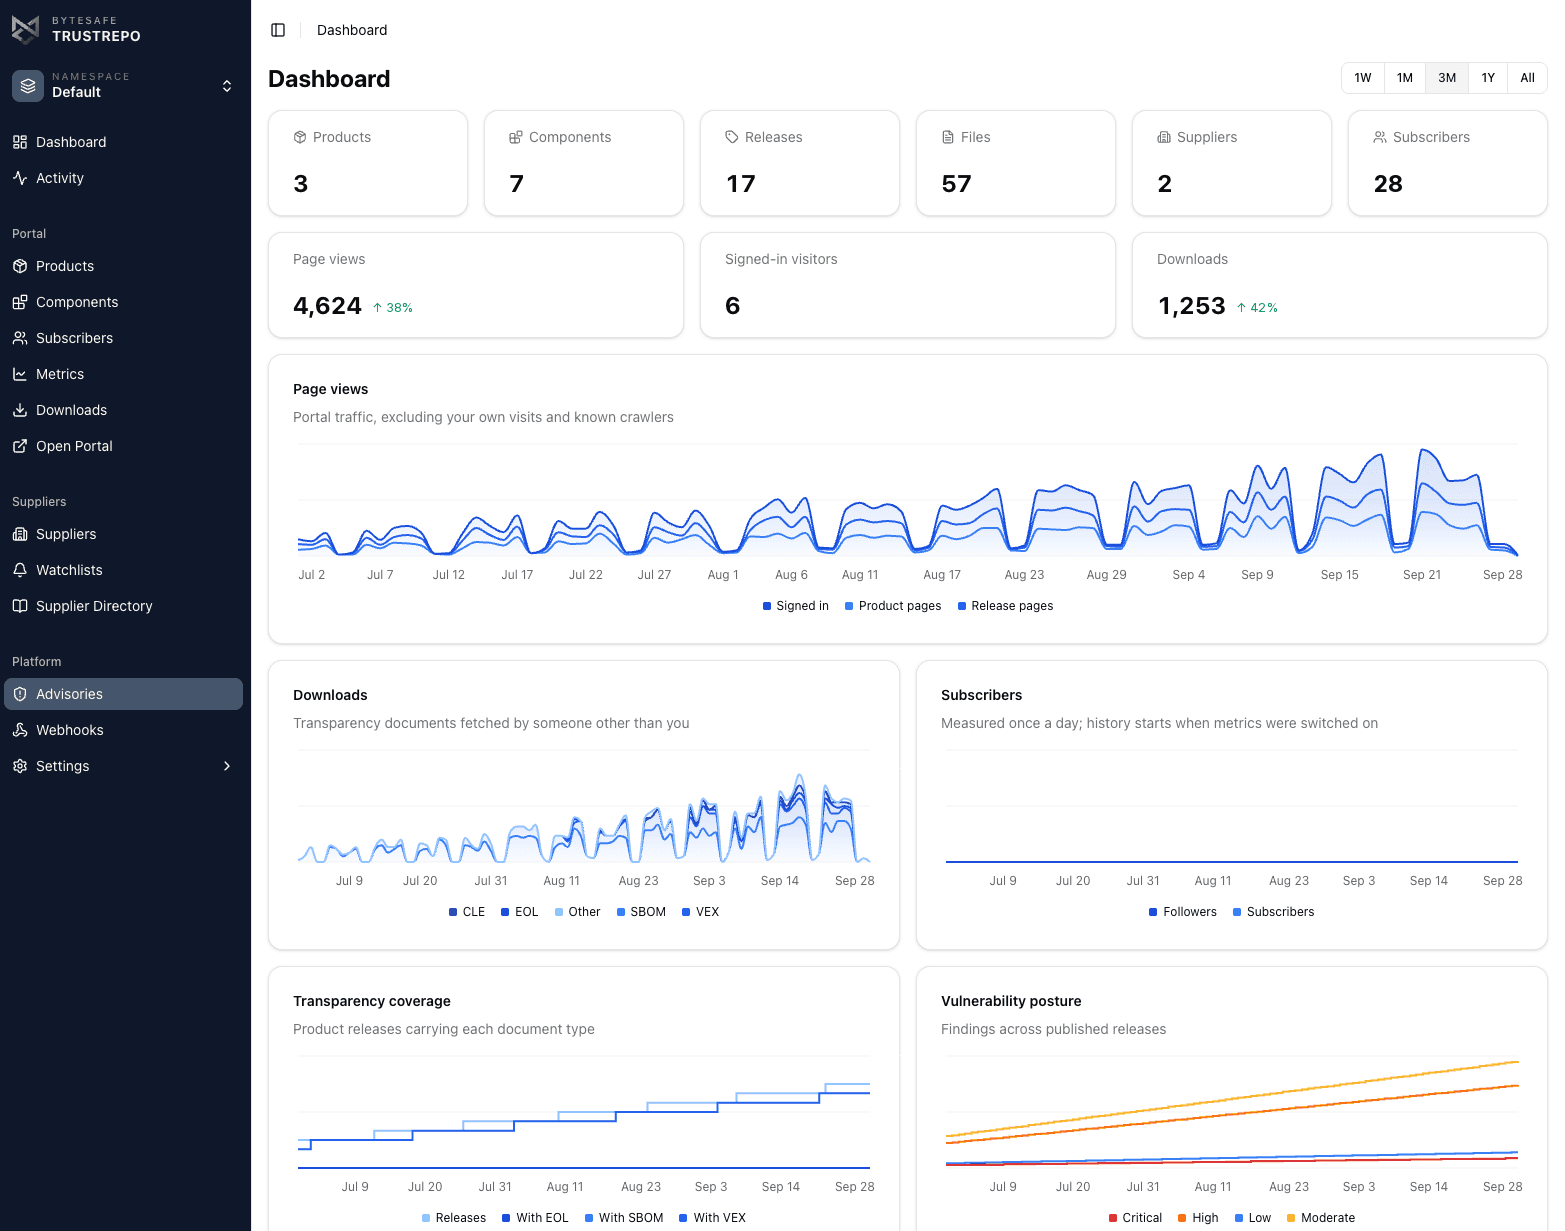
See who downloaded what
The dashboard counts page views, downloads by document type and subscribers. Signed-in downloads are recorded per document.
Who works with it
- Product and release teams
- Publish SBOM, VEX and release notes with each release.
- Sales and customer success
- Send customers a portal link when they ask for an SBOM.
- Security teams
- Decide what each customer sees and keep the VEX current.
Questions
Can we keep some products private?
Yes. A portal can be public or restricted to named organizations, and you choose which customers see which product.
Can we publish from CI/CD?
Yes. The REST API accepts SBOM, VEX and other documents with a scoped token. A token can be allowed to upload without being allowed to publish, and webhooks notify your other systems when something is published.
Which documents can customers download?
SBOM in CycloneDX and SPDX, VEX, lifecycle documents as ECMA-428, release notes and signatures.
Can we remove sensitive details before publishing?
Yes. The publishing pipeline can redact an SBOM before it reaches a customer.
Start with one supplier
In a demo we invite a supplier, publish a release and show what your customers download from the Trust Portal.