Supplier Transparency
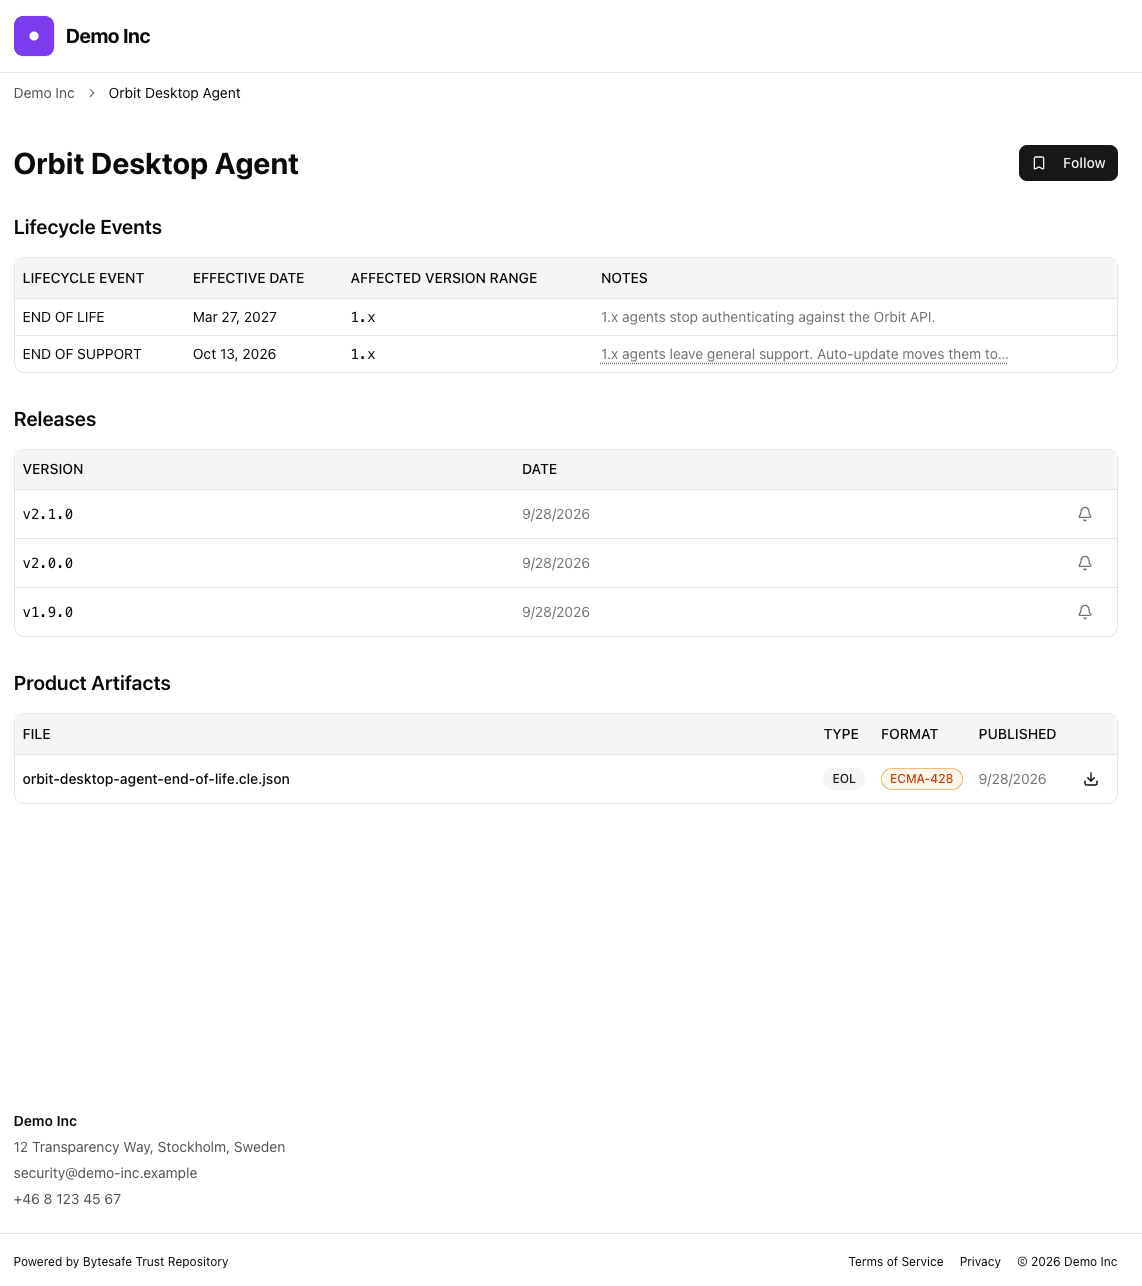
Collect SBOMs, VEX and end-of-life dates from your suppliers without chasing attachments. Each supplier publishes into its own space, and every document is checked on arrival and kept with the release it covers.
Supplier documents arrive by email
One supplier sends a CycloneDX SBOM, another a spreadsheet, a third a PDF from a penetration test. Each covers one release, and you ask again for the next.
- Nobody knows which file covered which release
- Documents sit in inboxes and shared folders, named by whoever saved them.
- Every release means asking again
- A new version ships and the follow-up emails start over.
- Nothing checks a document when it arrives
- An SBOM can list components with known vulnerabilities, and nobody notices until an audit.
- Some suppliers have nothing machine-readable
- A PDF assessment or a signed statement is all they can give you.
How it works with Trust Repository
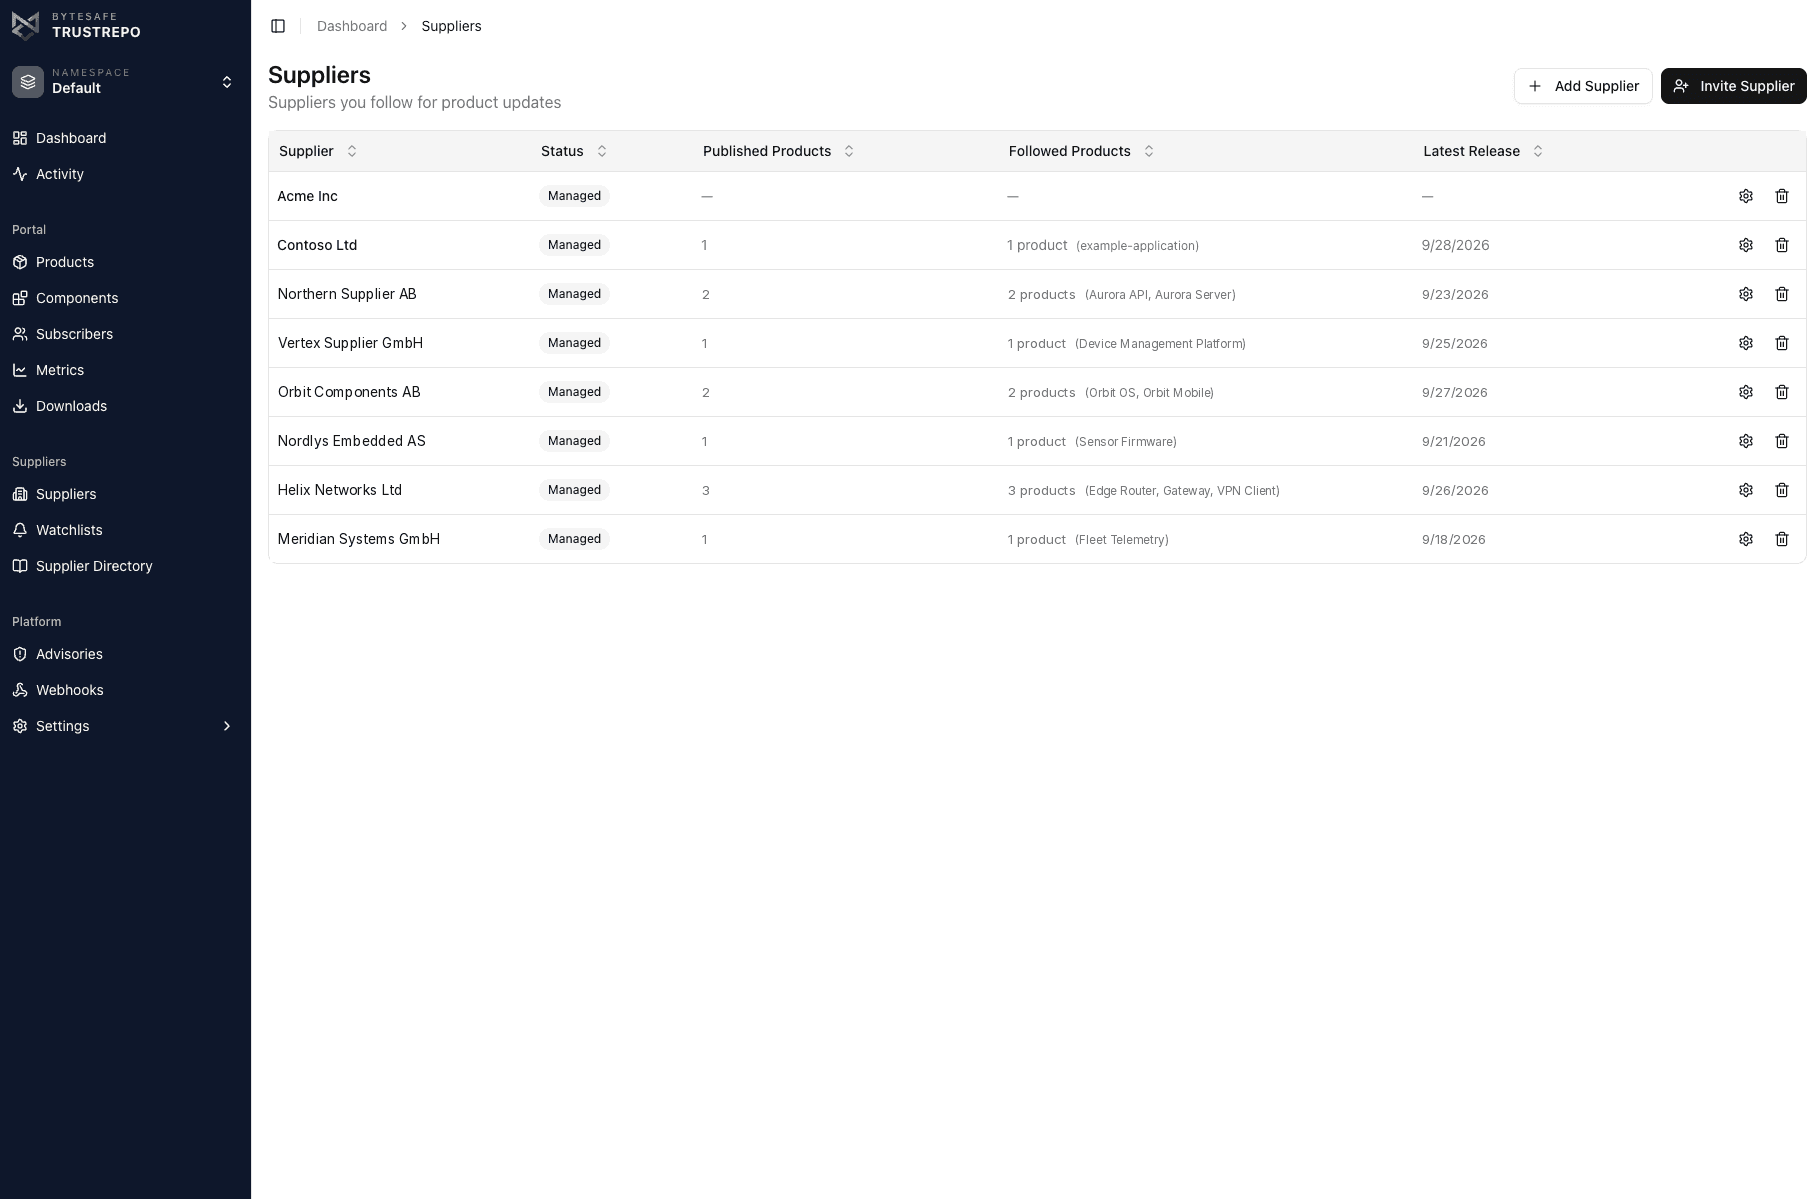
1Invite the supplier
Send an invite by email or a short code. The supplier gets its own space and sees only its own products.
2The supplier publishes
SBOM, VEX, end-of-life dates and release notes, from CI/CD over the REST API or by upload in the browser.
3You follow the releases
Each SBOM is checked against known advisories when it arrives. New releases appear in your activity feed.
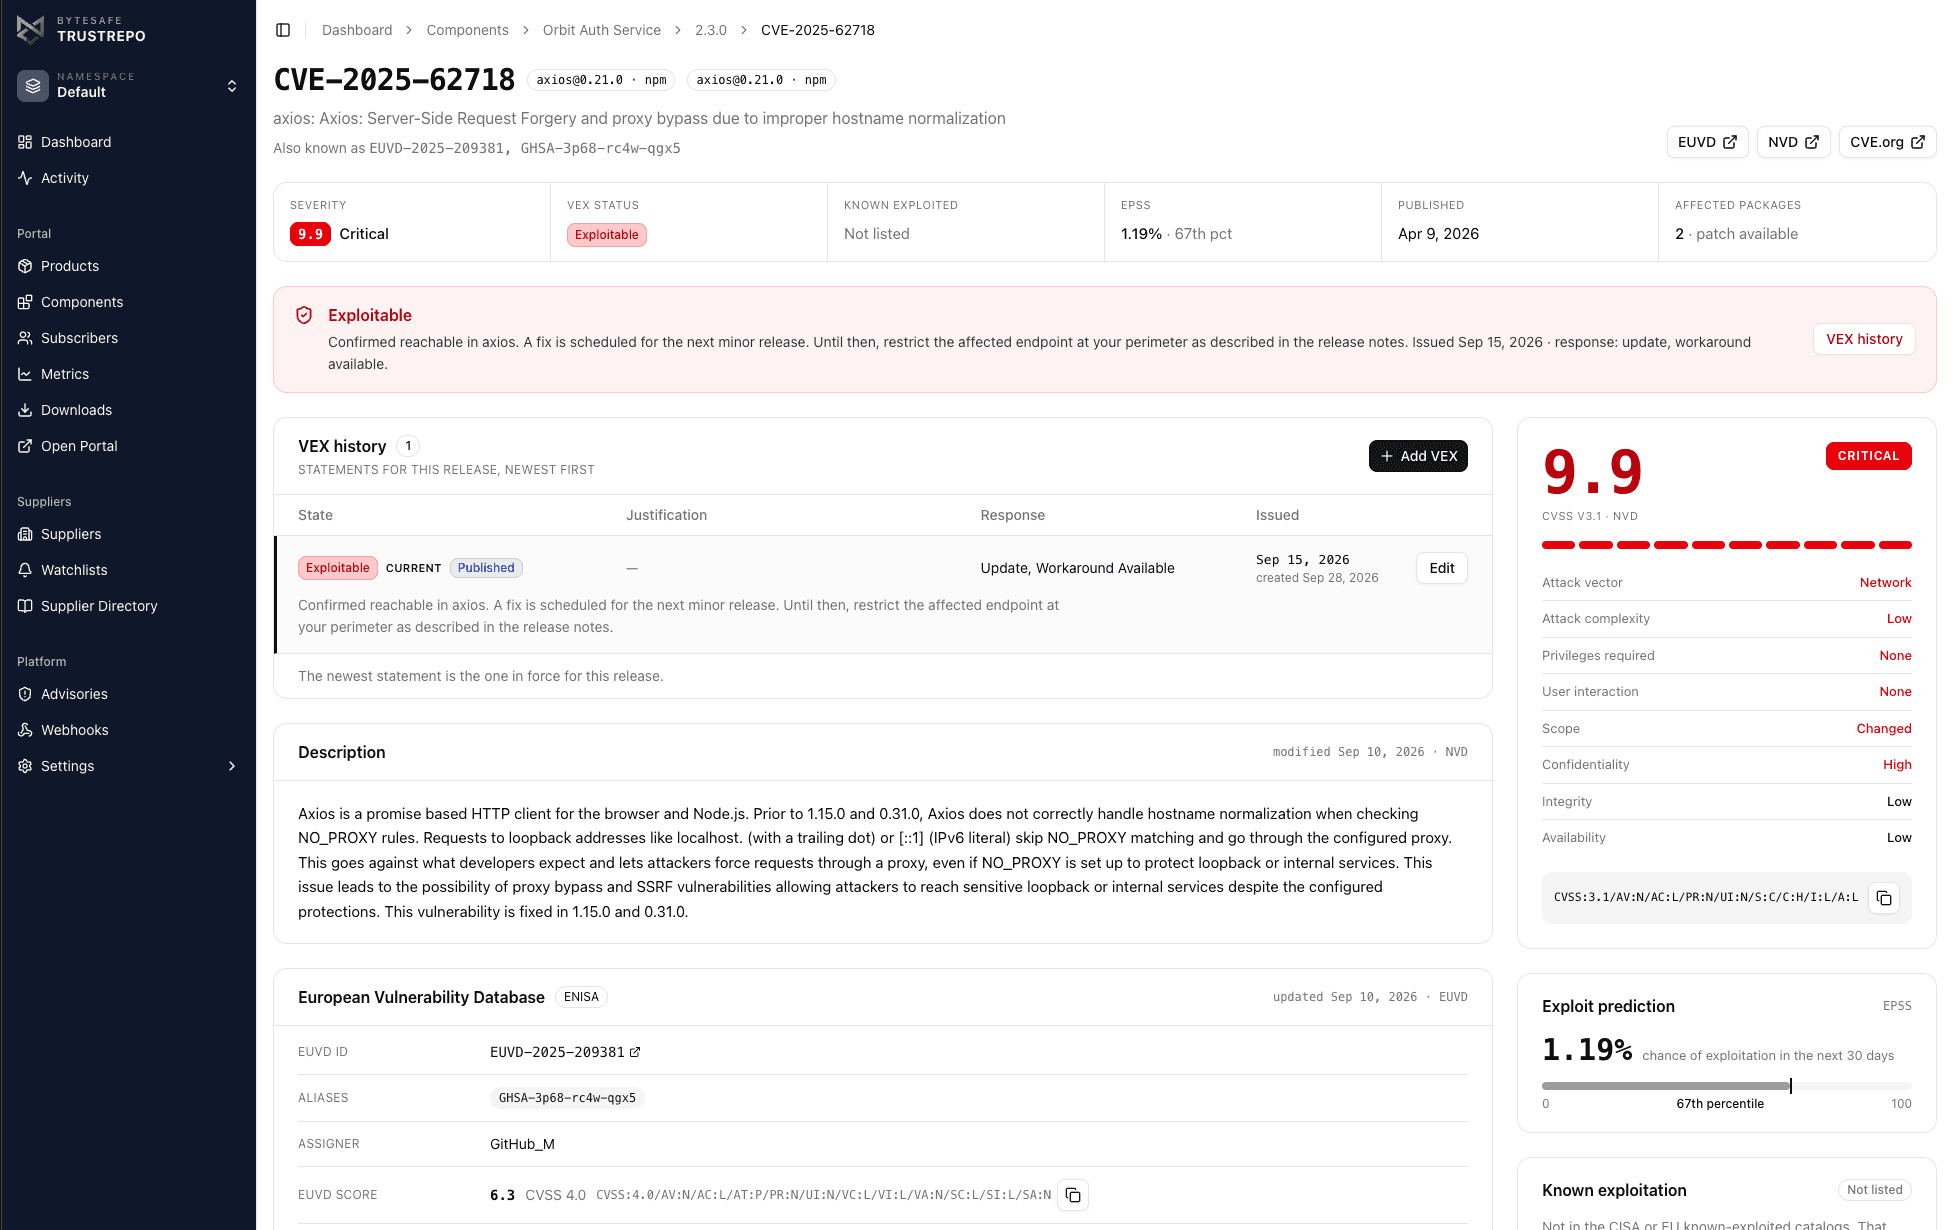
Findings on supplier releases
Each vulnerability shows severity, EPSS, KEV listings and the supplier's VEX statement. You can see whether the supplier considers it exploitable and what they plan to do about it.
Who works with it
- Procurement and vendor management
- Onboard each supplier once. New releases arrive without a request.
- Security teams
- See findings and the supplier's VEX for every supplier release.
- Compliance teams
- Show which supplier document covered which release, and when it arrived.
Questions
Do suppliers need access to our systems?
No. A supplier signs up to its own space and sees only its own products and releases. It needs no access to your CI/CD or repositories, and it cannot see your other suppliers.
What if a supplier cannot provide an SBOM?
Add the supplier yourself and upload what you have. A PDF assessment is stored as a dated record, and you can replace it with a real SBOM later without losing the history.
Can suppliers automate their uploads?
Yes. The REST API accepts SBOM, VEX and other documents from any CI system with a scoped token. Suppliers without a pipeline upload in the browser.
What happens to the documents if a supplier leaves?
Documents from a product you subscribe to are your data from the moment you subscribe. You keep them.
How does this relate to SBOM Observer?
Trust Repository collects the documents and checks them against known advisories. SBOM Observer adds impact analysis across your own and supplier software, and your own policies in CI/CD.
Start with one supplier
In a demo we invite a supplier, publish a release and show what your customers download from the Trust Portal.