Software Inventory
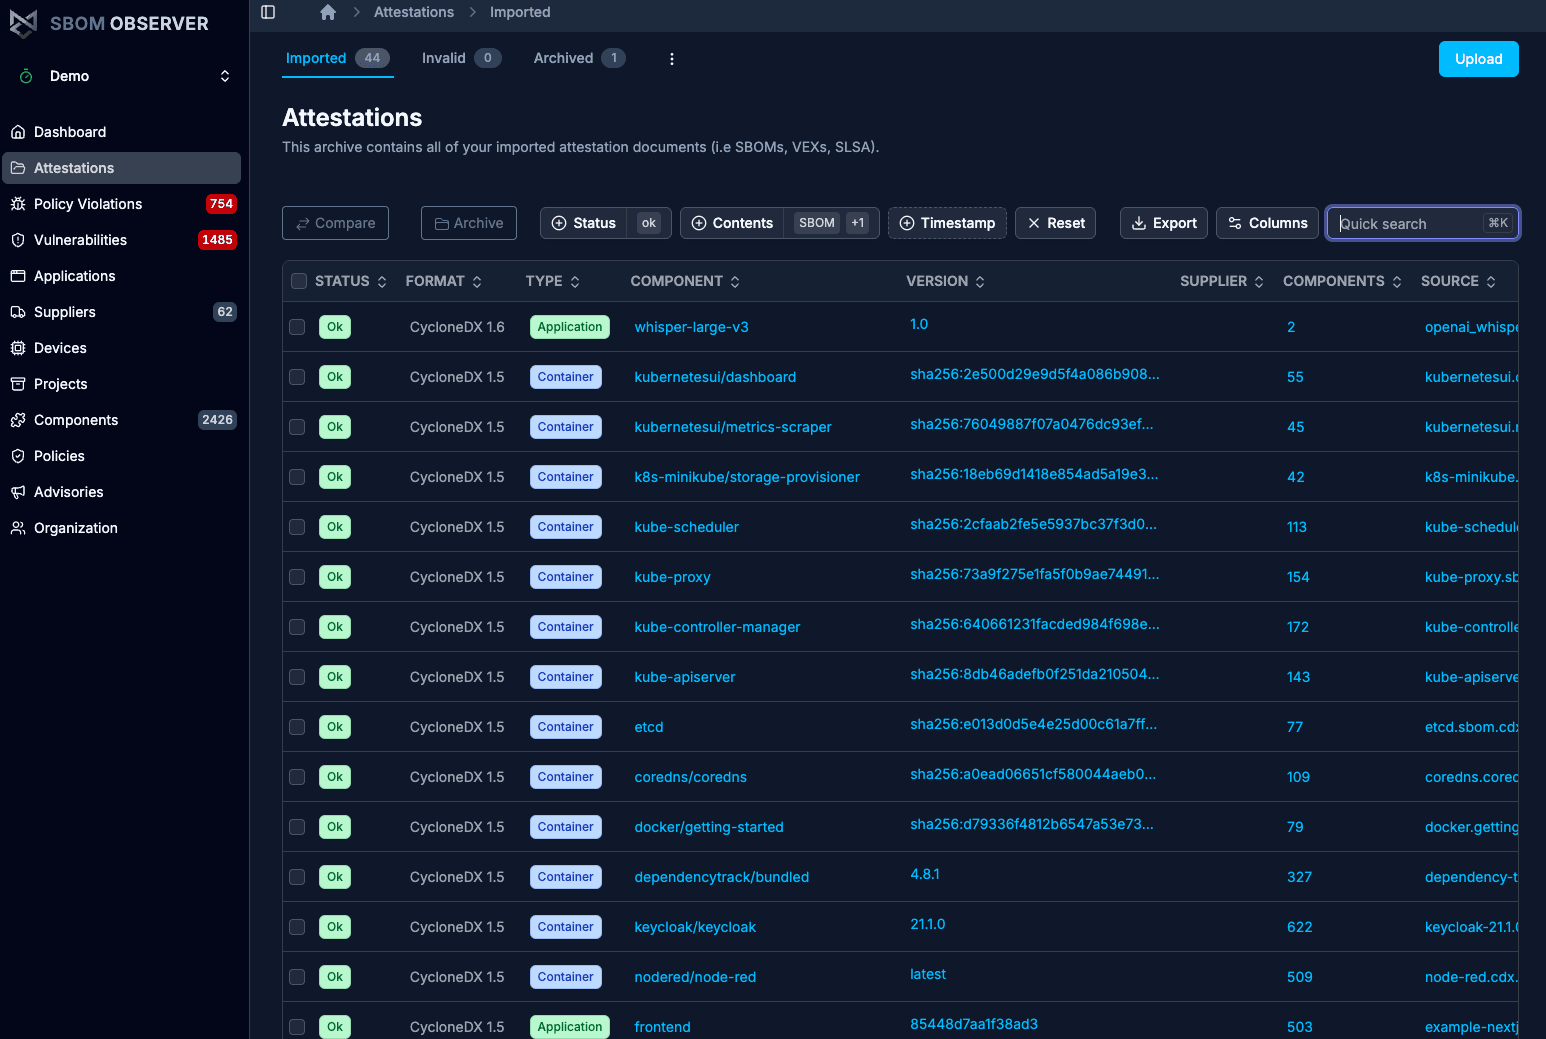
Build an inventory of applications, components and releases from the SBOMs your pipelines and suppliers produce. It updates on every build, down to the operating system packages inside your containers.
Software data lives in too many places
The asset database knows application names. The build system knows dependency versions. Supplier documents live somewhere else. Few teams can say what runs where today.
- Two pictures of the same software
- The CMDB lists applications. The build system knows dependency versions. Neither says what shipped.
- Vendor software tracked on the side
- Third-party software has its own spreadsheet and owners, and comparing it with internal software means merging lists by hand.
- Updated once a quarter
- Manual updates lag behind. New versions and components pile up in between.
How it works with SBOM Observer
1Connect the pipelines
The Observer CLI uploads an SBOM from each build, so new components show up with the build.
2Import what you have
CycloneDX and SPDX exports from SCA and asset tools load alongside, and supplier SBOMs by upload.
3Search by component
Find every application and release that ships a component version, with its license and known vulnerabilities.
Health of the projects you depend on
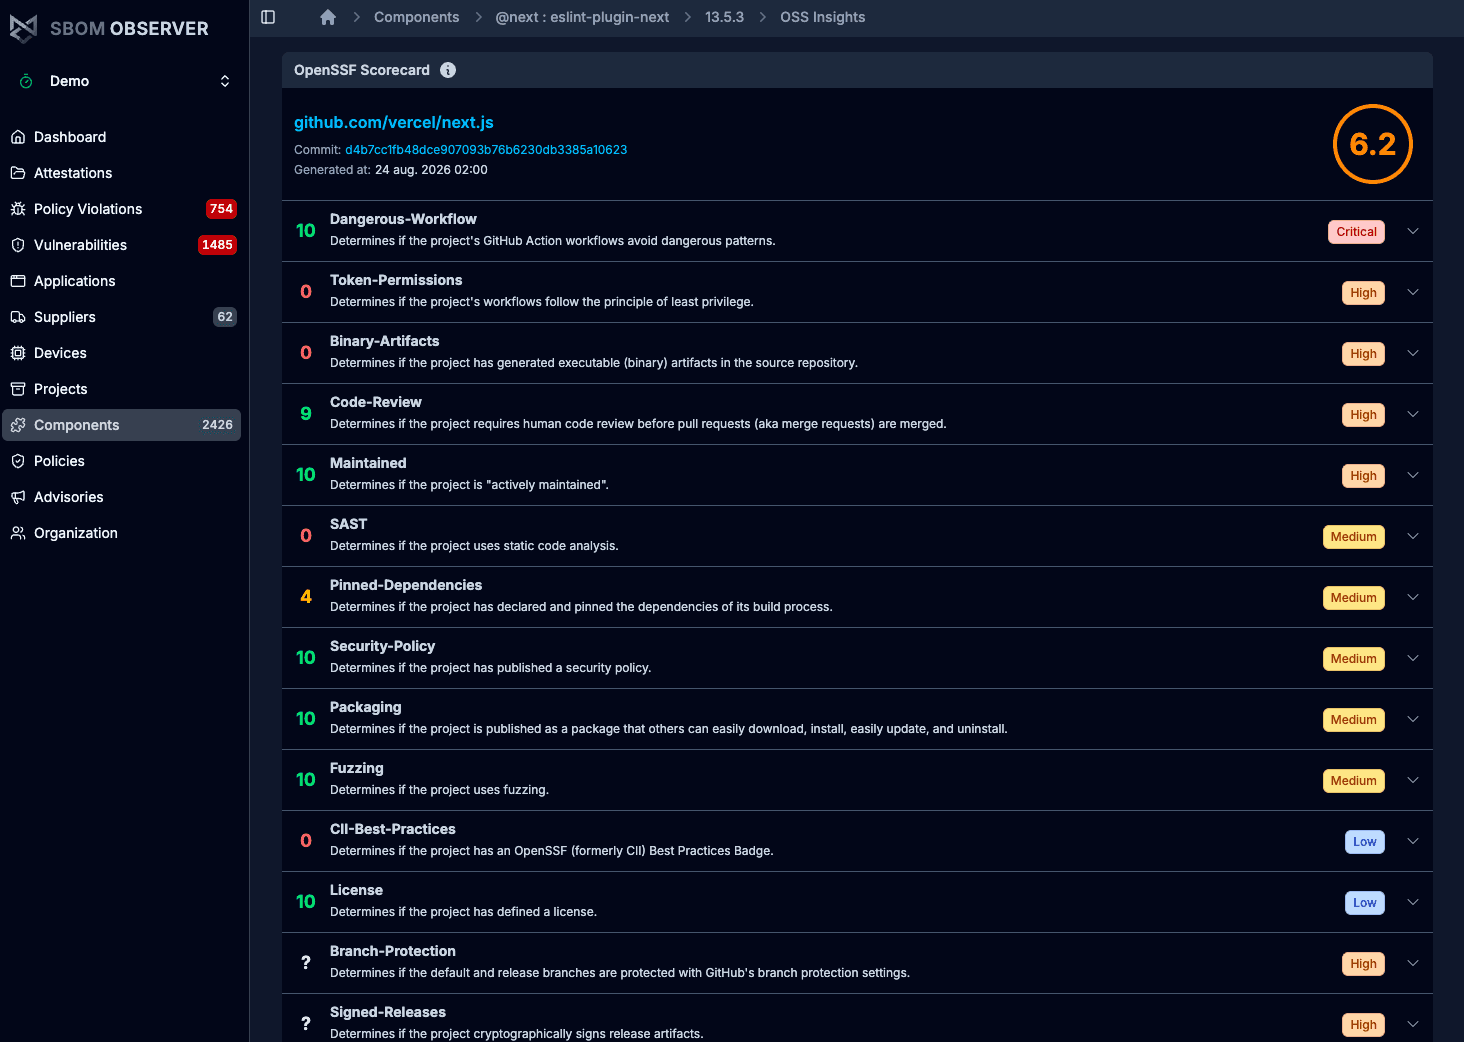
Each open source component shows the OpenSSF Scorecard of its source repository: maintenance, code review, token permissions and more.
Who works with it
- Application owners
- See what is in each release without waiting for a manual inventory update.
- Security and compliance teams
- Search the portfolio for a component version without running a new scan.
- Vendor management and procurement
- See vendor software next to internal builds, with no separate spreadsheet.
Questions
Can we import existing asset data?
Yes, as CycloneDX or SPDX exports from your SCA, CMDB or asset tools.
How current is the inventory?
As current as your pipelines. Each build that runs the Observer CLI uploads its SBOM.
Does it cover containers?
Yes. Container SBOMs are broken down by base image layer, operating system package and application dependency.
More SBOM Observer use cases
All use cases- SBOM ManagementCollect CycloneDX and SPDX from CI/CD and suppliers, and keep one SBOM record per release.
- Vulnerability ImpactSee which applications and releases a CVE affects, and record VEX decisions next to it.
- Regulatory ComplianceKeep SBOM, VEX and policy results per release for CRA, NIS2 and DORA.
- M&A and Due DiligenceReview an acquisition target or new vendor from its SBOMs.
Upload an SBOM from your own build
Click through the live demo with example data, or book a demo and bring your own SBOMs.