M&A and Due Diligence
Review acquisition targets, investments and new vendors from their SBOMs. See known vulnerabilities, licenses and dependency depth per product before the deal closes.
Due diligence runs on questionnaires
Acquirers and procurement teams get a spreadsheet of self-reported answers. Component-level risk stays hidden until after the deal.
- You see what the target chooses to share
- Questionnaires and interviews cover what the other side wants to discuss.
- No view of components or dependency depth
- You know the product name and language. You do not know which packages it ships or whether they have known CVEs.
- License problems found after closing
- A copyleft license three levels down the dependency tree now belongs to the product you bought.
How it works with SBOM Observer
1Request SBOMs
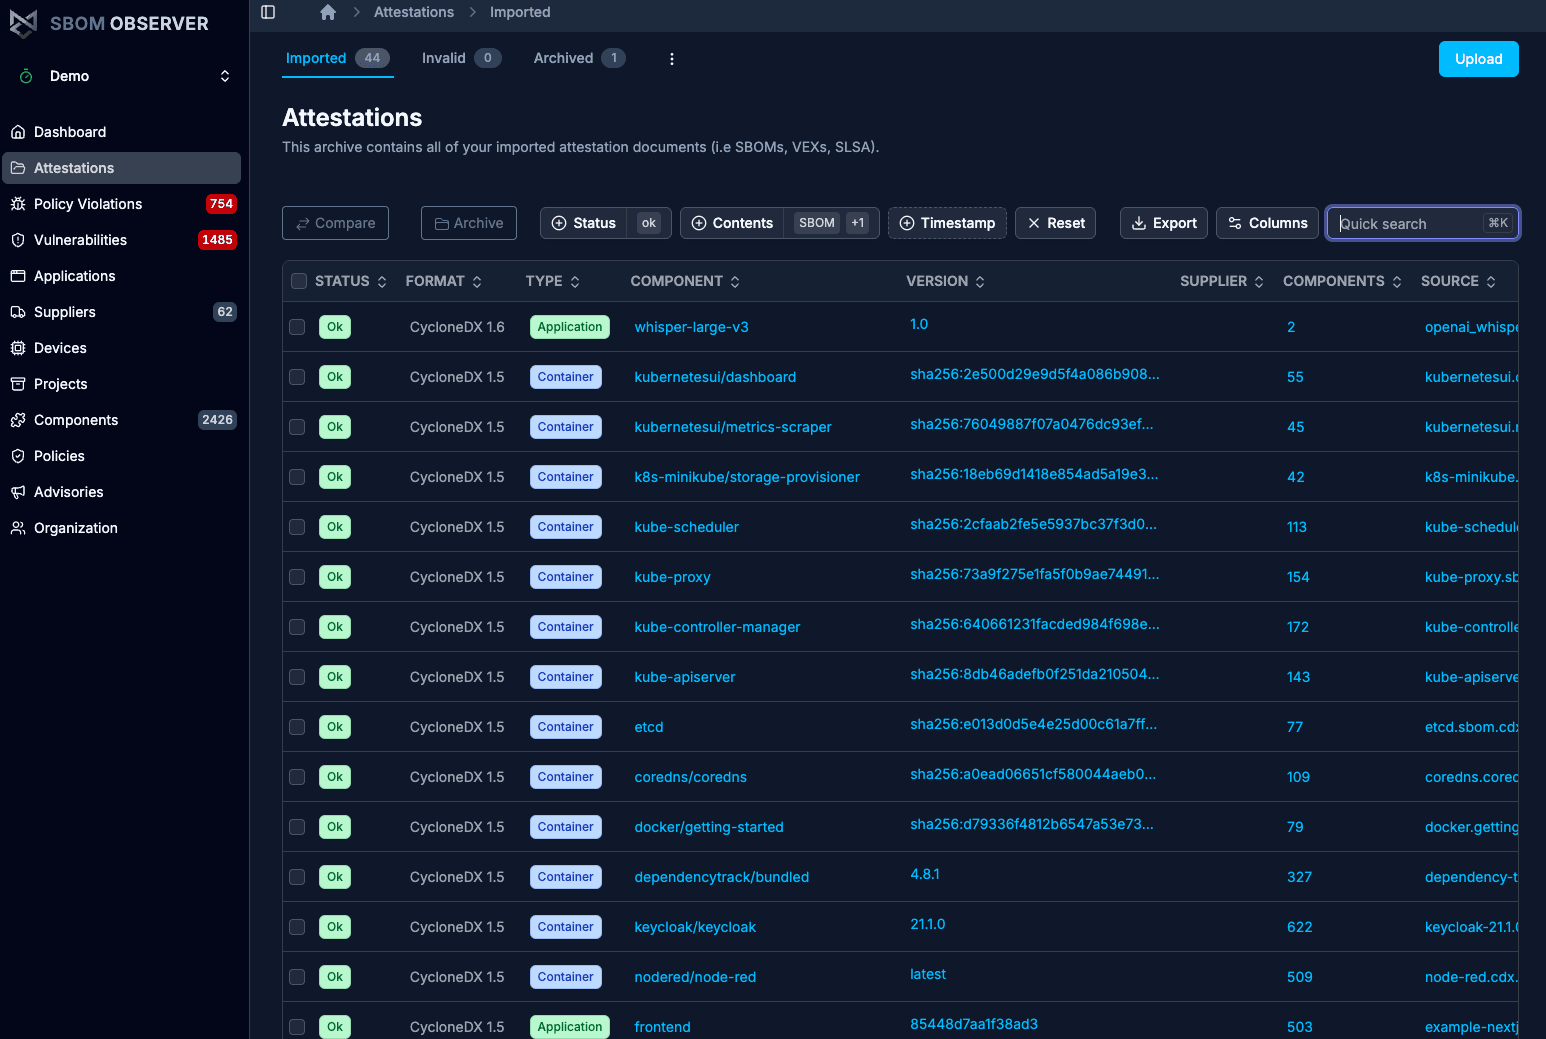
CycloneDX or SPDX per product. With access to source or build artifacts, the Observer CLI can generate them.
2Upload into a separate project
The target's SBOMs go through the same analysis and policies as your own software.
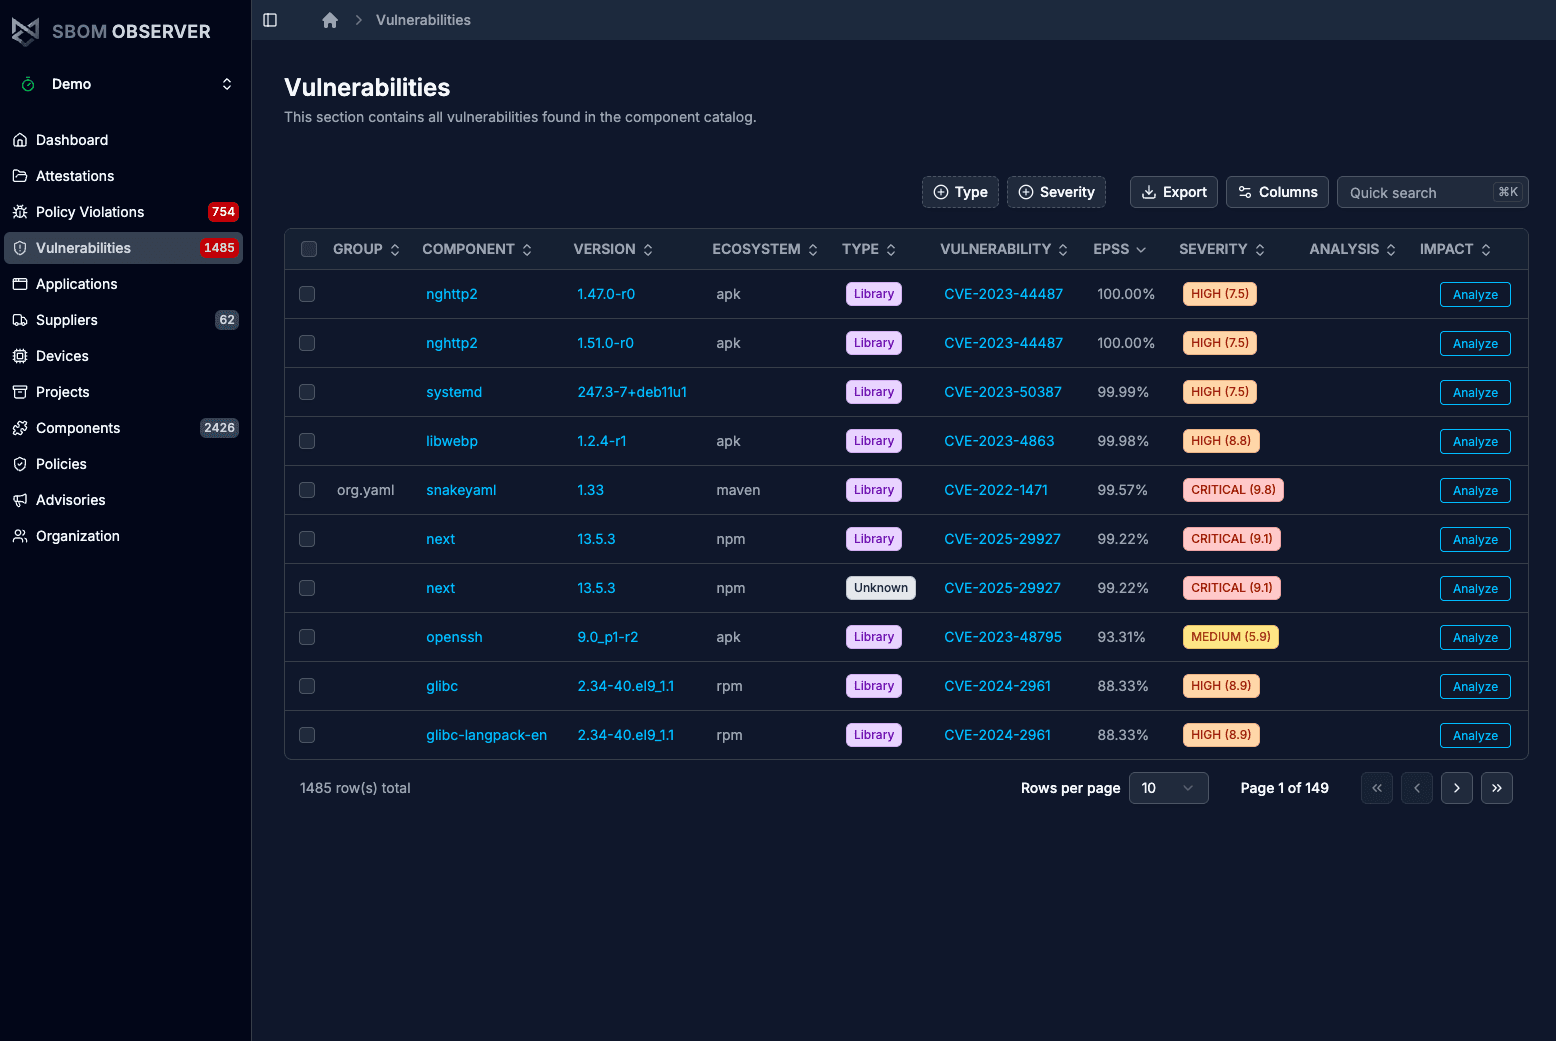
3Review findings per product
Known vulnerabilities by EPSS, license exposure and the health of the open source projects it depends on.
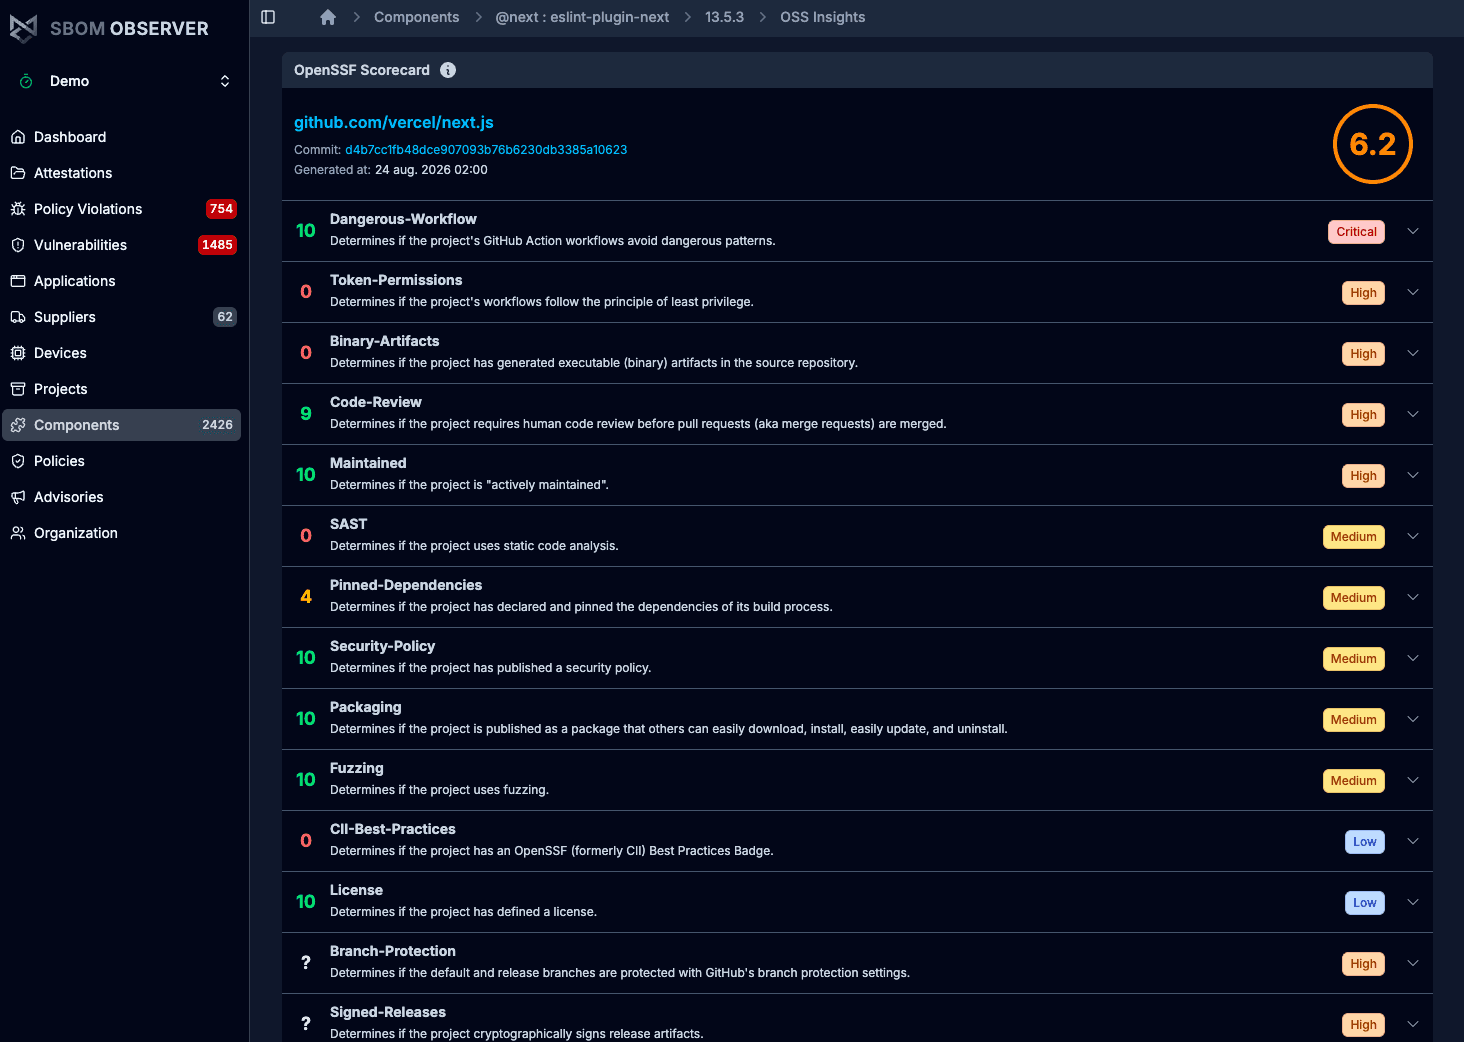
Project health of every dependency
The OpenSSF Scorecard shows whether the projects a product depends on are maintained, reviewed and released safely.
Who works with it
- M&A and investment teams
- See license exposure, outdated dependencies and known CVEs before the deal closes.
- Security and risk assessors
- Review target SBOMs with the same tool they use for internal software.
- Vendor onboarding
- Check new vendors' SBOMs with the same policies as every other supplier.
Questions
What if the target has no SBOMs?
With access to source or build artifacts, the Observer CLI can generate SBOMs from them. Without it, the missing SBOMs are a finding in themselves.
Can we run the review in an isolated environment?
Yes. On the Enterprise plan, SBOM Observer runs in private cloud and on-premises, including air-gapped.
Can we look at a single SBOM first?
Yes. The free SBOM Analyzer checks one CycloneDX or SPDX file for NTIA minimum elements, known vulnerabilities sorted by EPSS, and licenses. No signup.
Open the SBOM AnalyzerMore SBOM Observer use cases
All use cases- SBOM ManagementCollect CycloneDX and SPDX from CI/CD and suppliers, and keep one SBOM record per release.
- Vulnerability ImpactSee which applications and releases a CVE affects, and record VEX decisions next to it.
- Regulatory ComplianceKeep SBOM, VEX and policy results per release for CRA, NIS2 and DORA.
- Software InventoryOne inventory of components and releases across internal and supplier software.
Upload an SBOM from your own build
Click through the live demo with example data, or book a demo and bring your own SBOMs.